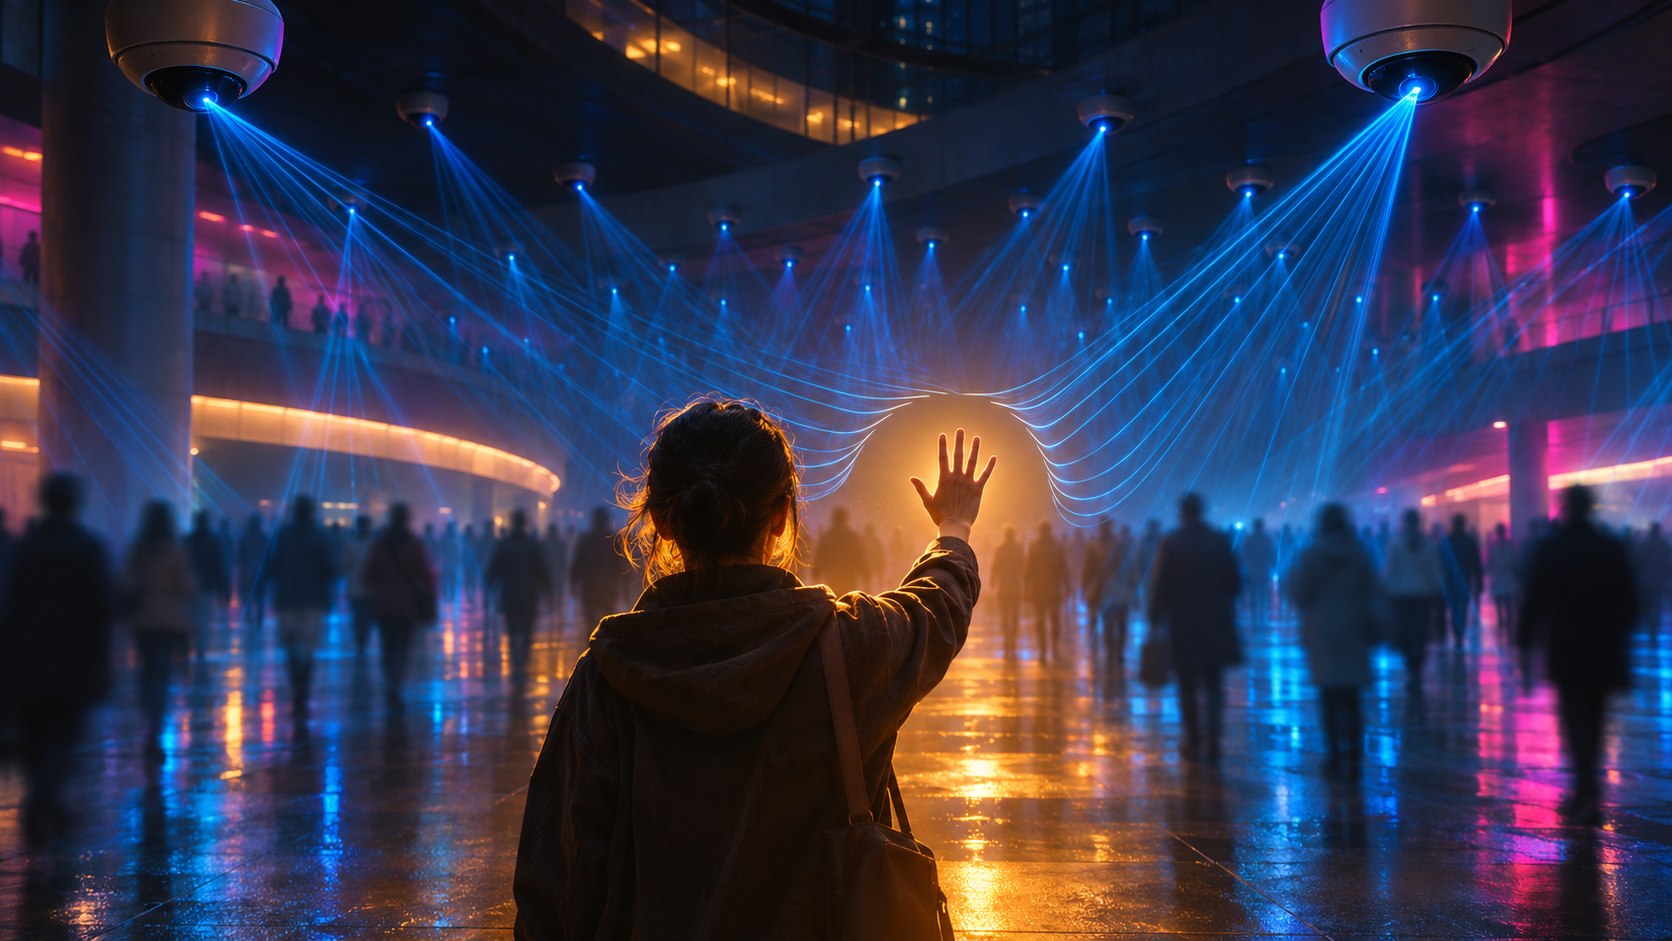
Picture a crowded station on a grey weekday morning. Hundreds of people pass a camera mounted above the ticket barrier. Most of them have never agreed to anything about their face. Yet somewhere in the system, each passing face is turned into a short string of numbers and compared with a list. Most people never learn that it happened, and most would not know whom to ask. That gap, between a face being read and a person being asked, is the subject of this essay.
How a machine learns a face
Facial recognition is software that finds a face in an image, converts it into a mathematical description, and compares that description with others. The description is often called a biometric template: a set of numbers that stands in for the face. Two photographs of the same person produce similar templates, and the software scores how close they are. A match is a probability, not a certainty, and the score depends on lighting, angle and the quality of the training data.
The training data is the root of the problem. A system that recognises faces must first learn from millions of them, and those faces have to come from somewhere. The answer, in several well-documented cases, is the public internet.
Clearview and the scraped face
Clearview AI built its database from images scraped from the open web. On 3 September 2024, the Dutch Data Protection Authority, known as the AP, announced a fine of EUR 30.5 million against Clearview AI over the database. The sources we read do not give the date of the underlying decision.
The AP's chair, Aleid Wolfsen, said: "Facial recognition is a very invasive technology that you can't just unleash on everyone in the world." Our reading: the point of the fine is not that a photograph of a face is secret. It is that a face collected at scale and matched without the person's knowledge is personal data, and the AP judged that the company's processing broke European data protection rules.
Our view: a fine is a strong signal, but it does not undo the database. The question for regulators is not only how much a company pays, but whether the scraped material can be removed from the systems that already use it.
Europe draws a line
The EU's AI Act takes a different approach. Its Article 5 lists practices that are banned outright, and one of them is the real-time remote biometric identification of people in publicly accessible spaces by law enforcement. The ban is not absolute. Commentary on the Act, including analysis by the Future of Privacy Forum, describes three narrow exceptions: searching for victims or missing persons, preventing a specific, serious, imminent threat to life or physical safety, and locating or identifying a suspect of an offence carrying a custodial sentence of at least four years. Each individual use requires prior authorisation from a judicial or independent administrative authority. The Forum also describes a narrow emergency route: where authorisation cannot be obtained before use, it may begin, but authorisation must be requested within 24 hours.
We have not checked the official text of Article 5 in the Official Journal for this essay. The description above comes from secondary commentary, and the wording should be checked against the text before it is quoted.
Critics are not satisfied. Reclaim The Net's headline reads "EU AI Act Effectively Legalizes Biometric Mass Surveillance." We could not read the article's body, so its full argument is unverified. That criticism is a fair one to test. A rule that permits a use under exceptions is not the same as a rule that stops it.
The American record: money, not prohibition
The United States has no federal equivalent. Our reading: the strongest tools have come from states and from courts. Texas sued Meta in 2022, in state court, over biometric data collected through the company's Tag Suggestions feature, which suggested who to tag in photographs. The suit relied on a 2009 state law that protects Texans' biometric data, such as fingerprints and facial scans. On 30 July 2024, Meta agreed to pay Texas USD 1.4 billion. Meta admitted no wrongdoing.
Illinois has a stricter law. Its Biometric Information Privacy Act has produced large settlements, and in 2021 Meta agreed to pay USD 650 million to settle a case under it. In the same year, Meta said it had shut down its facial recognition system on Facebook.
The pattern is telling. Both the Texas and Illinois cases ended in payments, and Meta admitted no wrongdoing in Texas.
Why "I agreed" does not work
The usual defence of face recognition is consent. Users agreed to the terms, the argument goes, and they could switch the feature off. The Tag Suggestions case shows how thin that is. Our view: most people who used Facebook probably had no clear picture that a face-matching system ran across their photographs, and a setting buried in menus does not amount to an informed choice.
Our view: consent is a poor tool for a technology whose main effect falls on people who are not in the room. A friend who posts a photo of a crowd has agreed to nothing on behalf of the strangers in it, and the people at the station never saw the terms at all.
Implications
Three groups carry most of the risk.
The first is people who never sign up for anything: passers-by, protesters, workers in the background of someone else's photograph. They bear the cost of recognition without any of the benefits.
The second is communities that already face heavier policing. Our view, not a sourced finding: an error in a police search has consequences that a wrong suggestion on a social network does not.
The third is the companies. Clearview and Meta show that fines and settlements have followed the collection of face data. Speculation, labelled as ours: if penalties stay smaller than the value of the data, the incentive will keep pointing toward collection first and apology later.
What could go wrong is clear enough. A database built for one purpose becomes available for another, and the people in it were never asked.
Conclusion: the watchers need watching too
The station camera does not ask anyone's permission, and it does not have to. The law can refuse to let it match faces in some places, fine companies that scrape the web, and demand that payments be made. None of those tools reaches the moment when a face is read in a crowd and no one is told. Consent cannot close that gap alone. A system that reads faces should have to justify itself to the people it reads, before it reads them.
Sources: Dutch Data Protection Authority fine on Clearview AI (announced 3 September 2024; the decision date is not given in the sources read), reported by Fortune (https://fortune.com/europe/2024/09/03/facial-recognition-clearview-fined-30-5-million-banned-invasive-ai-the-netherlands/) and Jurist (https://www.jurist.org/news/2024/09/netherlands-data-protection-authority-fines-us-ai-company-30-5-million-euros-over-facial-recognition-database); Future of Privacy Forum on the EU AI Act's restrictions on real-time remote biometric identification (https://fpf.org/blog/red-lines-under-the-eu-ai-act-restricting-real-time-remote-biometric-identification-systems-for-law-enforcement-purposes/); Verfassungsblog on the AI Act prohibition (https://verfassungsblog.de/ai-act-and-the-prohibition-of-real-time-biometric-identification/); Texas Tribune on the Meta settlement (https://www.texastribune.org/2024/07/30/texas-meta-facebook-biometric-data-settlement); Jurist on the Meta Texas settlement and the Illinois settlement (https://www.jurist.org/news/2024/08/meta-agrees-to-1-4b-settlement-with-texas-for-allegedly-violating-biometric-privacy-laws/).